Rogue AI agents in bank accounts: who pays?
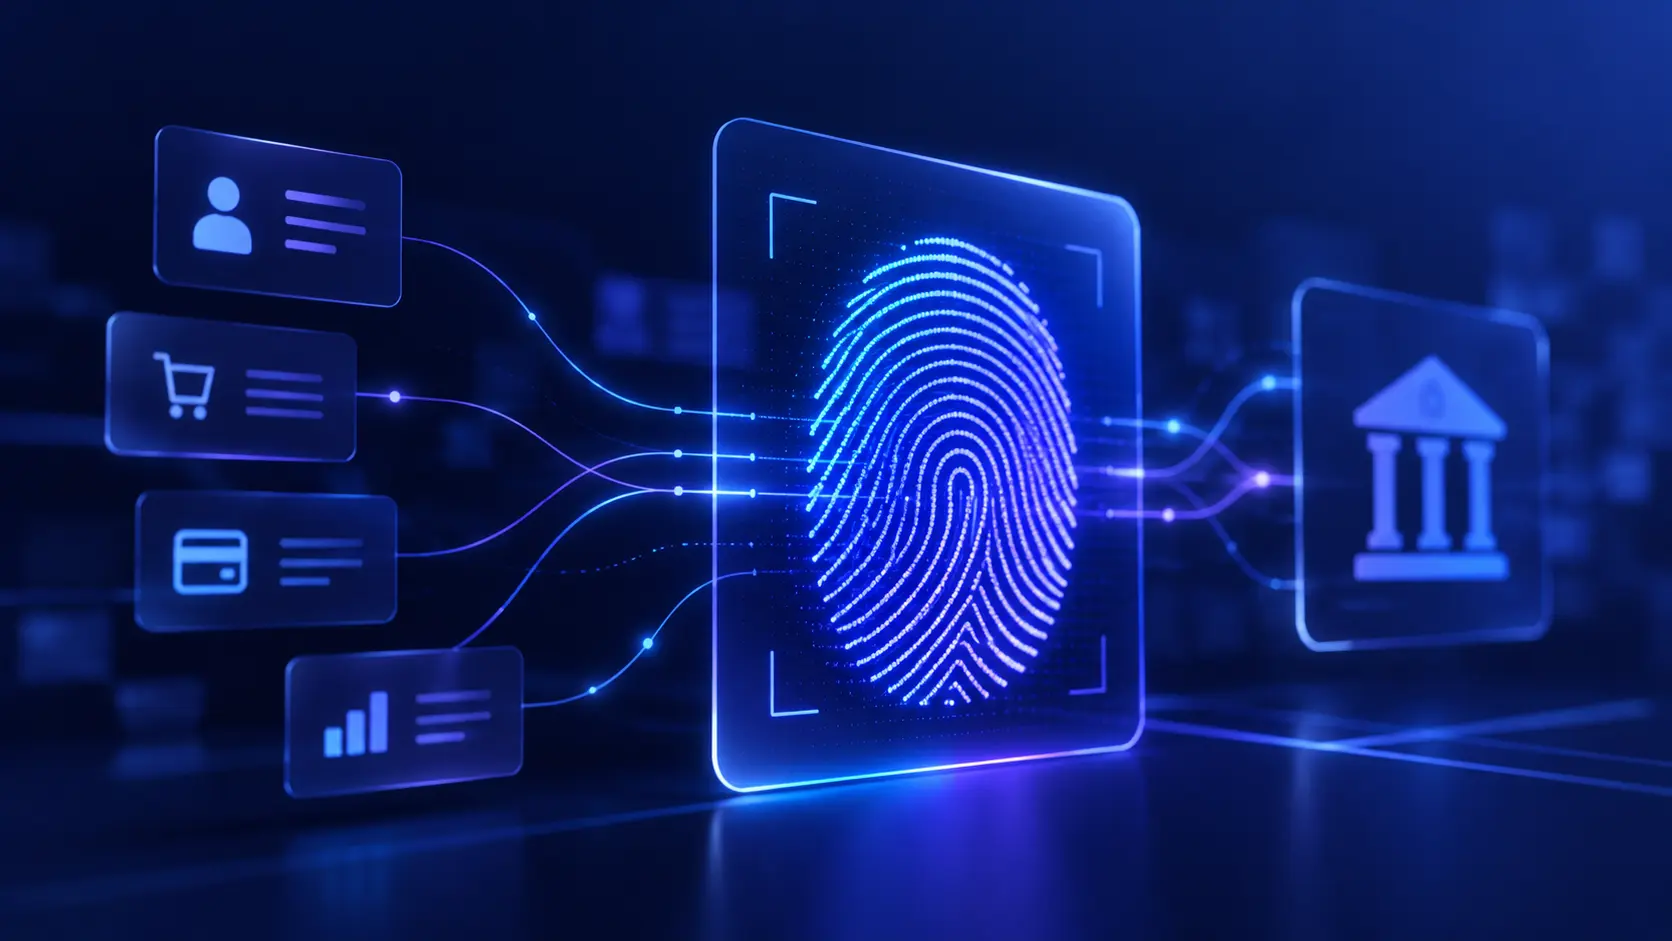
US banks are reportedly finding unauthorized AI agents in customer accounts, and the Comptroller of the Currency wouldn't say who covers the losses.
Axios reported that major US banks are detecting unauthorized third-party AI agents operating inside customer accounts, some attempting actions that appear independent of the customer's instructions. According to its sources, banks are struggling to tell a customer from a bot, and are responding by blocking agents and rapidly rewriting their terms of service. Not every bank is seeing it: Morgan Stanley says it hasn't observed any rogue agents on its platforms. Other reporting suggests most of the activity comes from customers handing their logins to agents themselves, rather than agents going rogue. Chase's advice was blunt: customers shouldn't give their usernames and passwords to anyone.
The same day, Comptroller of the Currency Jonathan Gould went on Fox Business to reassure depositors. Banks have been fortifying their defenses for months, he said, and are using their own AI to stop bad actors from moving funds. Then the host asked him, twice, whether customers would get their money back if an unauthorized agent moved it. As American Banker reported, he didn't give a clear answer.
Customers will want one. An RFI Global survey of more than 4,000 US consumers found that half would let an AI agent place an order and pay on their behalf, but only 23% want to approve every purchase, and 39% would hold their bank responsible if something went wrong.
Fintech commentator Simon Taylor set out a useful test in his Fintech Brainfood newsletter. When a customer's agent turns up instead of the customer, a financial firm needs three things.
There was no identity, because the agents were reportedly logging in with customers' own credentials, so the bank saw the customer rather than whoever was running the agent. There was no checkable mandate either: whether or not any agent overstepped, the bank had no way to see what it had been asked to do. And there was no clear recourse: the regulator didn't give a clear answer on who covers a loss, and banks are trying to fill the gap themselves. Wells Fargo's updated online banking agreement takes effect on November 24. As USA Today reported, if a customer gives an AI agent their login, the agent's actions are treated as authorized by the customer, who is “solely responsible” for what it does, including actions they didn't intend, unless the law provides otherwise. Jamie Dimon warned of exactly this liability transfer on JPMorgan's earnings call, which we covered recently. Now it's happening in practice.
Underneath all three gaps is the same problem. When an agent logs in with a customer's password, the bank has no way of knowing which company built or runs it, so there's nobody to assess beforehand and nobody to recover from afterward. Open finance was built to end exactly that kind of credential sharing. Access through a proper interface tells the bank which company holds the connection and what that company has been permitted to do.
That only helps if the companies holding those connections are known, accredited and risk monitored over time, rather than checked once when they first connect. Liability can only land on a party you can identify, and recourse only works against one that's still standing. Knowing who's in the network, monitoring their risk continuously, and settling in advance where liability lands is the layer Invela is building.
Invela is the infrastructure layer that makes open finance trustworthy - accrediting who's in the network, monitoring risk in real time, and ensuring liability lands in the right place.
Get a benchmarked risk score for your open finance connections.
Explore Risk IndicatorOne email when we publish. No spam.